Maersk confirms IT security incident involving data extraction
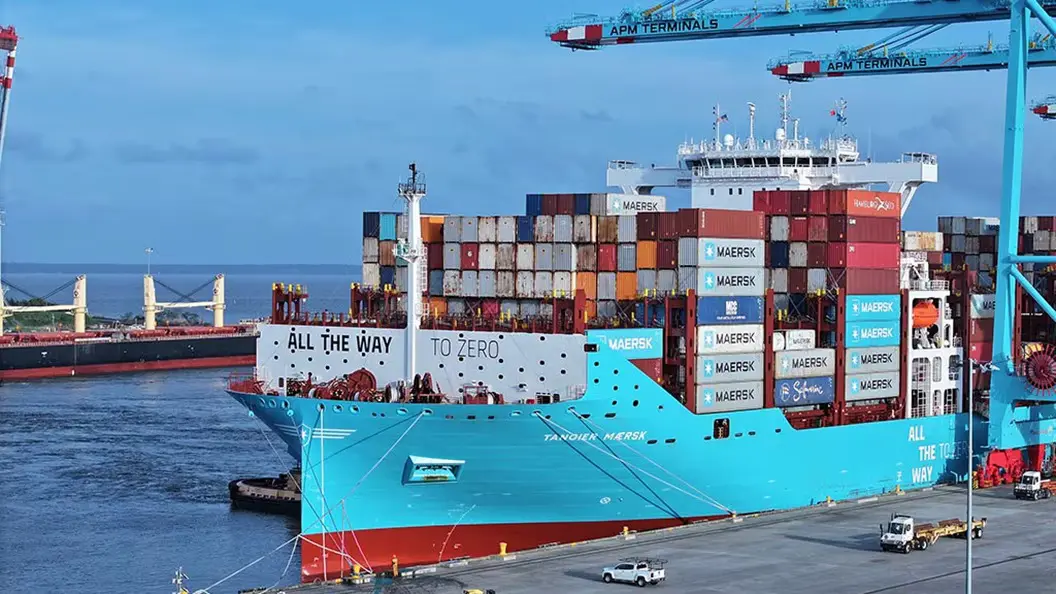
A.P. Moller–Maersk has confirmed an IT security incident involving unauthorised access and the extraction of data from a legacy system inherited through a previous acquisition, prompting an investigation by the Danish shipping group’s cybersecurity team.
In an official statement issued on November 11, 2026, Maersk said the affected environment was a local system and that immediate action had been taken to secure it. The company confirmed that its investigation remains ongoing, with initial findings suggesting that no sensitive data has been disclosed.
Maersk stated that it had found no indication of an impact on other internal systems or on customer and partner systems connected through application programming interfaces (APIs) and electronic data interchange (EDI). It also said it does not anticipate disruptions to customer operations, including the ability to book and manage shipments through its existing platforms.
Hacker group claims access to logistics data
The confirmation follows claims by a hacker group known as WhiteArmor that it had obtained approximately 100 gigabytes of data from a logistics platform associated with the former LF Logistics business, which was acquired and integrated into Maersk.
According to the group’s allegations, the material includes driver profiles, employee accounts, delivery records, warehouse information and shipment-related documentation. WhiteArmor has also reportedly demanded approximately $5 million in bitcoin, threatening to publish the alleged data if payment is not made by December 7.
These claims have not been independently verified. In particular, the reported volume of data, the alleged exposure of passwords and the identity of the party responsible for the incident have not been confirmed by Maersk.
The company’s official statement does not identify WhiteArmor or explicitly establish a connection between the group’s allegations and the security incident under investigation.
Maersk says customer operations remain unaffected
Maersk said its cybersecurity team launched a full investigation immediately after discovering the incident and is working to contain any potential consequences.
The company indicated that customers can continue using its digital platforms normally, while advising them to exercise caution when receiving unexpected communications claiming to concern the incident. Customers were encouraged to verify suspicious messages through their established Maersk contacts.
Maersk added that it would provide further information as its investigation progresses and notify affected parties if subsequent findings make such communication necessary.
The incident highlights the cybersecurity risks associated with legacy IT infrastructure in global logistics networks, particularly where systems inherited through acquisitions continue to support operational activities.
For now, the confirmed incident remains limited to unauthorised access and data extraction from a local legacy system, while the full extent of the exposure and any connection to the WhiteArmor claims remain unresolved.